This thread has been locked.

If you have a related question, please click the "Ask a related question" button in the top right corner. The newly created question will be automatically linked to this question.

Bus Fault exception is occurred.

Other Parts Discussed in Thread: SYSBIOS

Hi,

I met a exception situation.

I followed TI's  onchip OAD configuration for my project.

When I try to  add a code, bus fault exception is occurred.

For example, what i try to add code is below. 


#ifdef HAL_IMAGE_B_FACTORY
// Create clock to get batt level
Util_constructClock(&getBattClock, RippleBLE_clockHandler,
RS_FACTORY_BATTTEST_EVT_PERIOD, 0, false, RIPPLE_BATT_VAL_UPDATE_EVT);
#endif

Here is screen capture images from IAR IDE.

Bus fault exception is occurred on Boot ROM area.

Because R1 register is 0x00000000. 

Image #1 shows R1 register is 0x000000, Value for R1 is 0x00000000 on SRAM area (please refer to bottom memory area on #1 image)

I think that is the reason why exception is occurred.

For the reference, Image #3 show some value is loaded on R1 register. Therefore, there is no exception occurred.

It is just happened by adding/removing code above.

I have no idea why boot code can't load a value properly according to SRAM code area is changed by adding code.

Please, give me any comment. it will be very helpful.

If you need more information, please let me know.

Thanks in advance

<#1. Before but fault exception>

<#2. but fault exception>
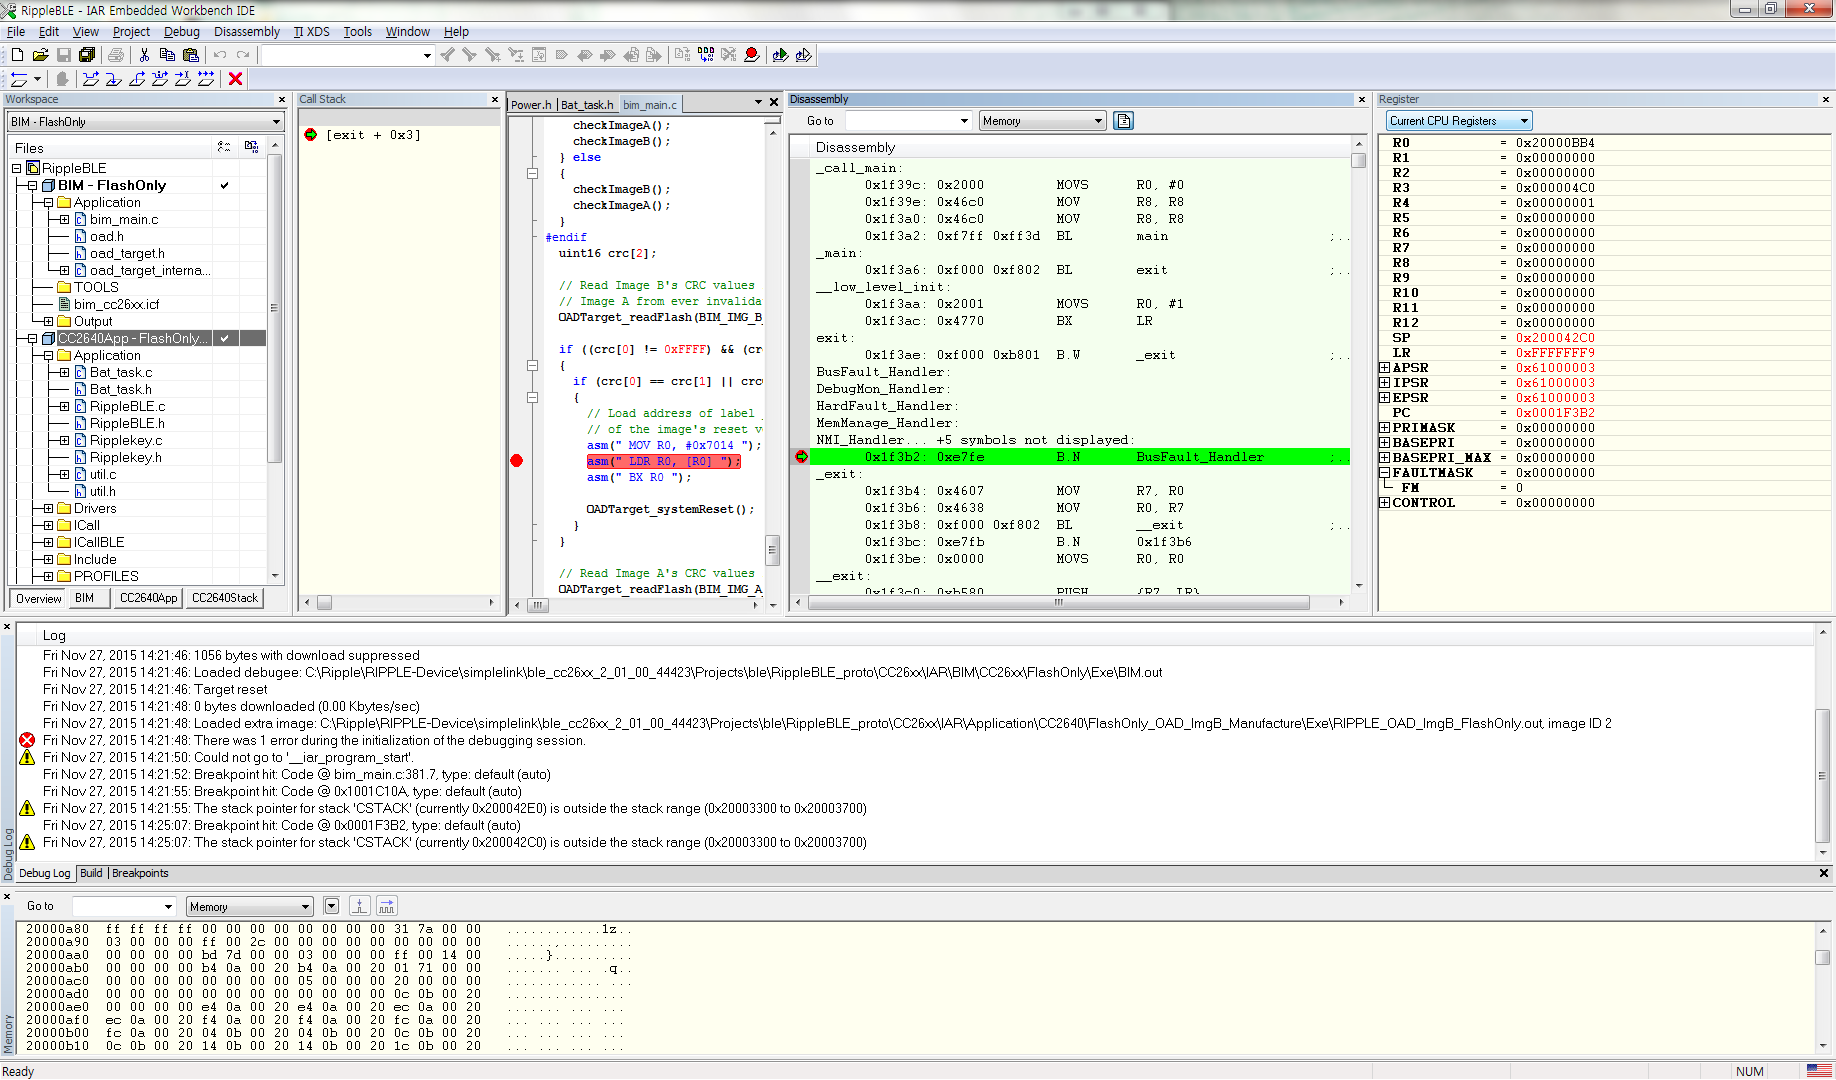
<#3. No exception>

  • Hello,

    Have you modified bim_main.c? Did you confirm that the address of __iar_program_start is at the location referenced in the asm code?

    Best wishes
  • Hello JXS,

     Yes, I changed address in bim_main.c. Also It looks OK.

     For your reference, I captured related things about  __iar_program_start.

    < bim_main.c>

    < memory dump>

    <Mapfile>

  • I add more information.

    It look some memory space is overlapped.

    In my first comment, it is refered 0x20000bb4 either exception and no-exception situation.

    It looks that  try to refer to data in <appBLE_prm3.orm3>

    But, in case of exception situaion, it looks that refer to wrong address.

    That's the reason why load value on R1 is 0x00000000. As a result, exception is occurred.

    It looks i missed something.

    Please guide me to fix this situation.


    <No exception situation>

    map file

    .data inited 0x20000b68 0x1c mangled__BIOS_lib.obj [10]
    .data inited 0x20000b84 0x18 RSprofile.o [1]
    .data inited 0x20000b9c 0x18 RSprofile.o [1]
    .data inited 0x20000bb4 0x18 appBLE_prm3.orm3 [2]
    .data inited 0x20000bcc 0x14 RSprofile.o [1]
    .data inited 0x20000be0 0x14 RSprofile.o [1]
    .data inited 0x20000bf4 0x10 devinfoservice-ripple.o [1]
    .data inited 0x20000c04 0x10 RSprofile.o [1]

    memory dump

    <exception situation>

    map file

    .data inited 0x20000b8c 0x1c mangled__BIOS_lib.obj [10]
    .data inited 0x20000ba8 0x18 RSprofile.o [1]
    .data inited 0x20000bc0 0x18 RSprofile.o [1]
    .data inited 0x20000bd8 0x18 appBLE_prm3.orm3 [2]
    .data inited 0x20000bf0 0x14 RSprofile.o [1]
    .data inited 0x20000c04 0x14 RSprofile.o [1]

     Memory dump


    Thanks,

      Chongchun Moon

  • Hi,

    I don't have full visibility into what you have changed, but I agree it looks like your App linker is overlapping with the BIM's memory area.

    How is 0x20000bb4 getting loaded. Let's start there and figure out why 0x20000bd8 is not loaded.

    Best wishes
  • Hi,

    I found why that value is loaded.

    'ti_sysbios_heaps_HeapMem_Object__table__C' symbol(address 0x04C0) has 0x20000bb4 value.

    Please refer to data below.  ti_sysbios_heaps_HeapMem_Object__table__C is located fixed area. 

    That area is not updated. Therefore, values in that area isn't changed.

    but, address of ti_sysbios_heaps_HeapMem_Object__table__V in exception case is changed.

    That's the reason why exception is occurred.

    I think that address of  ti_sysbios_heaps_HeapMem_Object__table__V shouldn't be changed.

    But, so far, I don't know how to avoid that situation.

    Please give me any comment.

    For your information, Image A area is 0x0600-0x6ffff , B area is page 7 ~ page 14(0x07000~0x14FFF), and Stack area is  Page 15~ Page30.

    Almost same as reference in SDK.

    <Image B map file - exception case> 

    ti_sysbios_heaps_HeapMem_Object__table__C
                                                           0x000004c0 0x4 Data Gb appBLE_prm3.orm3 [2]

    ti_sysbios_heaps_HeapMem_Object__table__V
                                                          0x20000bd8 0x18 Data Gb appBLE_prm3.orm3 [2]

    <Image B map file - no exception case>

    ti_sysbios_heaps_HeapMem_Object__table__C

                                                           0x000004c0 0x4 Data Gb appBLE_prm3.orm3 [2]

    ti_sysbios_heaps_HeapMem_Object__table__V
                                                          0x20000bb4 0x18 Data Gb appBLE_prm3.orm3 [2]

    <Image A map file>

    ti_sysbios_heaps_HeapMem_Object__table__C
                                                            0x000004c0 0x4 Data Gb appBLE_prm3.orm3 [2]

    ti_sysbios_heaps_HeapMem_Object__table__V
                                                           0x20000bb4 0x18 Data Gb appBLE_prm3.orm3 [2]

    Thanks,

      Chongchun Moon

  • HI,

    Base on my investigation above,  it looks some of member should have fixed address.

    So, I have tried to update linker file to keep that address.

    I added  "--keep ti_sysbios_heaps_HeapMem_Object__table__V" in CC26xx_link_iar.xdt file which is located at "\tirtos_simplelink_2_13_00_06\products\bios_6_42_00_08\packages\ti\sysbios\rom\cortexm\cc26xx\golden\CC26xx"

    and I checked linker.cmd  is updated and also map file is updated as below.

    Unfortunately,  address of that is not fixed. same as before.

    * map file is updated as below

    # ti_sysbios_family_arm_cc26xx_Timer_Module__state__V --keep
    # ti_sysbios_heaps_HeapMem_Object__table__V --define_symbol
    # memcpy=0x1001ca79 --define_symbol memset=0x1001ca8b --define_symbol

    * But address is not fixed at specific section.

    ti_sysbios_heaps_HeapMem_Object__table__V
                           0x20000bd8 0x18 Data Gb appBLE_prm3.orm3 [2]

    .data inited 0x20000b8c 0x1c mangled__BIOS_lib.obj [10]
    .data inited 0x20000ba8 0x18 RSprofile.o [1]
    .data inited 0x20000bc0 0x18 RSprofile.o [1]
    .data inited 0x20000bd8 0x18 appBLE_prm3.orm3 [2]
    .data inited 0x20000bf0 0x14 RSprofile.o [1]
    .data inited 0x20000c04 0x14 RSprofile.o [1]

    Here are the questions as below.

      Is that kind of approach is right way to resolve this situation by adjusting linker related file?

      If so, why isn't that member fixed? Please let me know where i need to modify to get fixed address.

    Thanks,

       Chongchun Moon