Part Number: BOOSTXL-CC2650MA
Hello,
I am working on a custom Bluetooth Low Energy project, for this purpose I used the TI multirole project. Until now I have used the just work pairing without bonding. Now I wont to exchange security key that I can establish a encrypted connection. My device (master) and the slave did not have a keyboard or a Display which allows the input of key. So I think the only way to use the Bondmanager is just works pairing and bonding enabled without mitm protection.
I have read have the chapter 5.4.3 of the Developers Guide SWRU393D. I configured my Gapbond manager with the following commands:
      uint8_t pairMode = GAPBOND_PAIRING_MODE_INITIATE;
      uint8_t mitm = FALSE;
      uint8_t bonding = TRUE;
      // set pairing mode
      GAPBondMgr_SetParameter(GAPBOND_PAIRING_MODE, sizeof(uint8_t), &pairMode);
      // set authentication requirements
      GAPBondMgr_SetParameter(GAPBOND_MITM_PROTECTION, sizeof(uint8_t), &mitm);
      // set bonding requirements
      GAPBondMgr_SetParameter(GAPBOND_BONDING_ENABLED, sizeof(uint8_t), &bonding);

      // Register and start Bond Manager
      VOID GAPBondMgr_Register(&multi_role_BondMgrCBs);
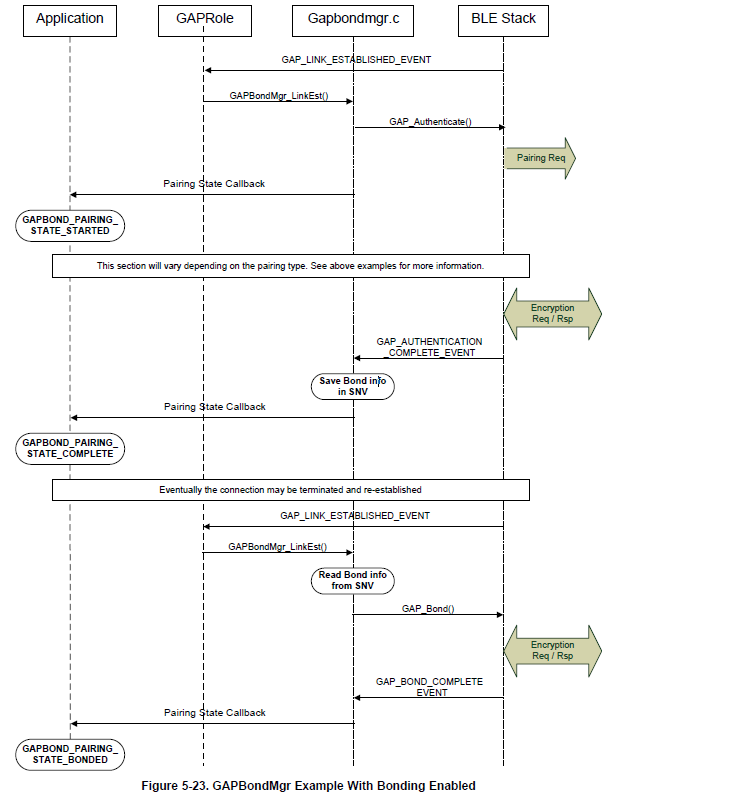
In the picture below and in the developers guide is described that in the initial pairing, bonding process a GAPBOND_PAIIRNG_STATE_COMPLETE event is processed from the stack. In future connections this event is not processedthe stack process a GAPBOND_PAIRING_STATE_BONDED (This means the stack has load the keys from the flash). Now my problem when I connect to a device I receive a GAPBOND_PAIRNG_STATE_COMPLETE Event. When I disconnect the device and reconnect I also receive a GAPBOND_PAIRNG_STATE_COMPLETE Event. I think I should now receive a GAPBOND_PAIRING_STATE_BONDED event. So I think my device did not save the encryption key in the Flash.
Could you tell me how I can figure out if my device has stored the keys in the flash? And how can I figure out if they are used for further connections with this device.
The second question is: Can I choose other options to prevent the connection against mitm attack? (Both devices have no keyboard and no Display)