This thread has been locked.

If you have a related question, please click the "Ask a related question" button in the top right corner. The newly created question will be automatically linked to this question.

AM263P4-Q1: ECC error injection

Part Number: AM263P4-Q1

I prototyped ECC detection for OCSRAM based on the following ECC MSS L2 sample. However, after calling the SDL_ECC_injectError function, there are cases where the ESM callback function is invoked and cases where it is not.
https://software-dl.ti.com/mcu-plus-sdk/esd/AM263PX/09_02_00_56/exports/docs/api_guide_am263px/SDL_ECC_PAGE.html#autotoc_md1214

I have two questions.
(1) Is there a possibility that if testLocationValue = injectErrorConfig.pErrMem[0]; hits the cache, it does not access the actual memory and therefore fails to detect the error?
If yes, wouldn’t it be necessary to disable the cache before the error injection test code, and then re-enable it afterward, as shown below?
If not, please explain the possible causes why the callback function is not invoked and the corresponding countermeasures.

CacheP_wbInvAll(CacheP_TYPE_ALL);
CacheP_disable(CacheP_TYPE_ALL);
__asm__ volatile ("" ::: "memory"); /* memory barrier */
SDL_ECC_injectError(...);
__asm__ volatile ("" ::: "memory"); /* memory barrier */
testLocationValue = injectErrorConfig.pErrMem[0];
CacheP_wbInvAll(CacheP_TYPE_ALL);
CacheP_enable(CacheP_TYPE_ALL);
(2) In the 2‑bit error sample, there is code that specifies the bit pattern to flip for error injection, such as:
injectErrorConfig.flipBitMask = 0x30002;

The value 0x30002 flips 3 bits rather than 2 bits. Is there any specific reason for this? The comment states “2 bit error,” but since it actually affects more than 2 bits, is it intentionally using 3 bits for testing?
Also, if we simply use 0x03 to flip only 2 bits, would we obtain the same result?

  •  Hi Imaoka,

    Apologies for the delayed response!

    All our examples have cache enabled only, so i don't think it is because of cache.

    My suggestions:

    Hardware ECC initializations are very important for this testing, so

    1. Always make sure to have "Bootloader_socInitL2MailBoxMemory" API in your bootloader code:

    This API will be helpful to initialize entire L2RAM memory and its corresponding ECC area with default values.

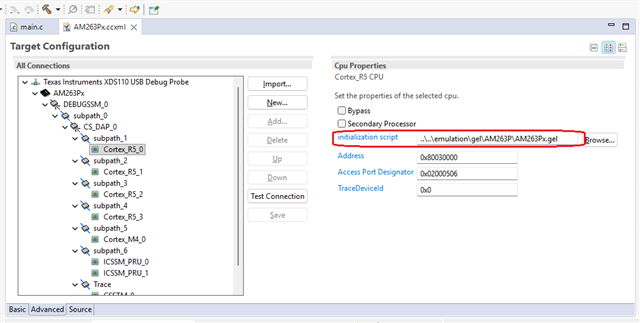
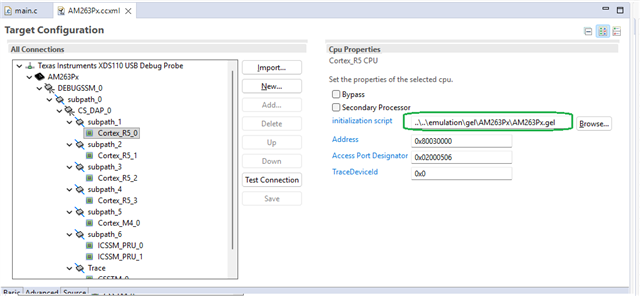
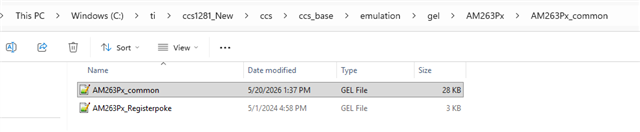
    1. If you are testing without bootloader and using dev boot mode, then in old versions of CCS i found Gel path is wrong:

    The path should be:

    If this gel path is not correct then the initializations that i mentioned in step-1 will not happen in dev boot mode.

    3. And also, for AM263Px devices make sure proper value that is 0x3F in initializations:

    Because we found it is just 0xF for some old versions of devices, that means only 4 banks are initialized instead of all 6 banks in OCSRAM.

    --
    Thanks & regards,
    Jagadish.

  • * I am posting this on behalf of the customer, Imaoka-san because it seems they are facicng issue on E2E. 

    (message from the customer)

    Hi Jagadish,

    The following code was created by us based on the sample code.
    The difference from the sample code is that, for the purpose of checking the memory content, we added the line
    testLocationValue = injectErrorConfig.pErrMem[0]; before calling SDL_ECC_injectError().

    When this line is commented out, error detection works as expected.

    We previously received a response stating that cache is not the cause of the issue.
    In our implementation, however, could cache be affecting the behavior?

    ****************************************************************************************

    SDL_ErrType_t retVal;
    SDL_ECC_InjectErrorConfig_t injectErrorConfig;
    volatile uint32_t testLocationValue;

    /* Note the address is relative to start of ram */
    injectErrorConfig.pErrMem = (uint32_t*)(a_addr);


    /* Run one shot test for sprcified memory x bit error */
    injectErrorConfig.flipBitMask = a_flipBitMask;

    testLocationValue = injectErrorConfig.pErrMem[0];

    __asm__ volatile("" ::: "memory");

    retVal = SDL_ECC_injectError(a_aggr, a_id, a_type, &injectErrorConfig);

    __asm__ volatile("" ::: "memory");

    if (retVal == SDL_PASS)
    {
    /* Access the memory where injection is expected */
    testLocationValue = injectErrorConfig.pErrMem[0];
    }

    ****************************************************************************************

    Regards, Imaoka

  • Hi Imaoka,

    You are right in that case the issue is because of cache only. And i tested and i can be able to reproduce your issue at my end as well.

    As you can see i added, injected error location reading before injection and i can see that there is no ESM call back that means detection is not working at all.

    So, you are right about this issue.

    I made below work around to work it again.

    Invalidated the cache before reading the location again like as shown below:

    /*Invalidate the location of error injected memory*/
    CacheP_inv((uint32_t *)&injectErrorConfig.pErrMem[0], sizeof(uint32_t), CacheP_TYPE_ALLD);

    As you can see now it is working as expected.

    --
    Thanks & regards,
    Jagadish.

  • Hi Jagadish,

    I was able to gain a good understanding of ECC error injection. Thank you very much for your support.

    Regards, Imaoka.