


Part Number: PROCESSOR-SDK-LINUX-AM62A
I am working on Secure Boot for TI AM62x (AM62A) and noticed a clear behavioral difference between ti-processor-sdk-linux-am62xx-evm-08.06.00.42 and ti-processor-sdk-linux-am62xx-evm-11.02.08.02 regarding the A53 U-Boot signing and authentication flow.
According to AM62x_Secure_SDK_v1.pdf, the documented process for A53 U-Boot is:
A53 u-boot binary and DTBs build using "am62x_evm_a53_defconfig“
each binary is individually signed by calling “$TI_SECURE_DEV_PKG/scripts/secure-binary image.sh”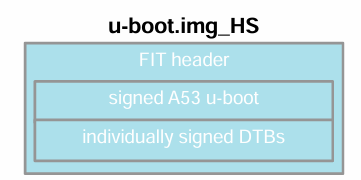
In Processor SDK Linux AM62xx 08.06.00.42, the actual behavior fully matches the documentation.
Observed behavior in SDK 11.02.08.02
After upgrading to 11.02.08.02, I observed the following differences:
-
During U-Boot build, there is no requirement to configure
TI_SECURE_DEV_PKG. -
In the build output, the following files are generated:
-
u-boot.img -
u-boot.img_unsigned
-
-
I do not observe the invocation of
secure-binary-image.sh.
However, on HS devices, booting with u-boot.img still works correctly.
Question 1: How is u-boot.img signed in SDK 11.02?
Question 2: Is there a recommended way to verify that u-boot.img contains valid authentication data?
Question 3: Is authentication of u-boot.img fully handled by TIFS?
- While reviewing the SDK 11.x U-Boot source code, I noticed the following call path:
arch/arm/mach-k3/security.c
    ----ti_secure_image_post_process()
          ----proc_ops->proc_auth_boot_image()