


Part Number: AM6442
Hi Champs,
I am seeking your answers for some questions below.
- My understand is that KEK is programmed into HS device at TI factory (correct me if I am wrong). I want to retrieve derived keys for encryption/decryption in my application. Looking at the 2 messages:
TISCI_MSG_CRYPTO_GET_DKEK https://software-dl.ti.com/tisci/esd/latest/2_tisci_msgs/security/dkek_management.html
TISCI_MSG_CRYPTO_GET_DSMEK https://software-dl.ti.com/tisci/esd/latest/2_tisci_msgs/security/dsmek_management.html
Can they return derived keys when the device is at HS-FS state? How about HS-SE state? - The above messages must be transferred over secure transport mechanism as per TI spec. To do this, secure Host ID and secure thread is a must. My application is running on A53 core and I understand that the FW (Linux or other OS) is running at non-trust zone, hence the access to secure transport is limited (or prohibited). I tried to implement the above TISCI messages but assert is observed. Is it feasible to implement the above message in A53 core? If yes, can you share with us how to do that?
- I can't find any sample implementation for Secure Management messages in TI SDK. Can you share some?
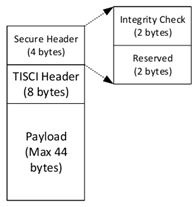
- For TISCI messages transmit over secure transport, Secure Message Header must be included with checksum calculated on HS device. As I can see, the algorithm is not available in TI SDK nor public documents. Where/How can I get the information?
Regards,
Kien

