


Part Number: AM62P-Q1
Hello Ti Expert,
As we know, the HS-SE device will mandatory execute Secure Boot. will follow the sequence as:
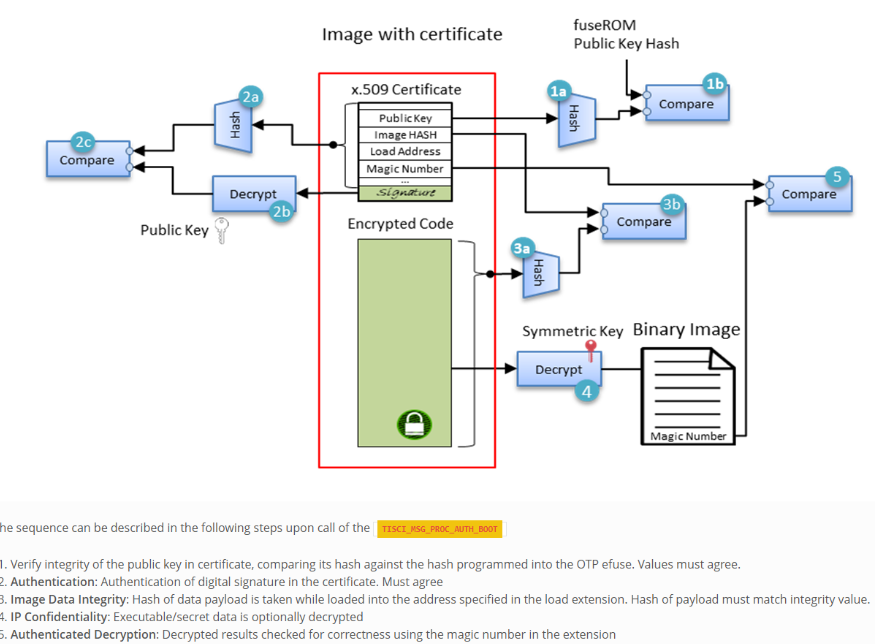
If the device is HS-FS, because eFuse don't have public key hash, if we send TISCI msg of " TISCI_MSG_PROC_AUTH_BOOT" to TIFS, whethe it also handle the sequence?
We test the secure boot on FS device, tampered a byte of iamge file: xxx.appimage.hs_fs, but finally the boot sequence failed.

So we guess in FS device, even if eFuse don't have public key hash, the above secure boot sequence, still hanldled, but only the first step of "public hash verification" is skipped?
Please help to confirm, Thanks!
B.R
